

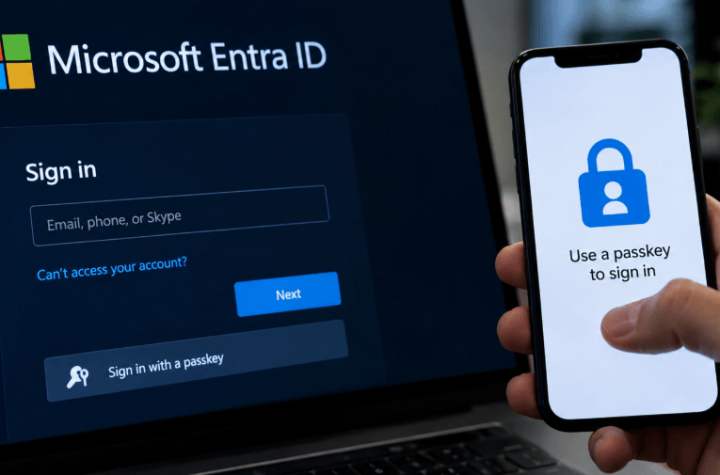
Microsoft is reminding organisations using Entra ID to move users towards phishing-resistant authentication methods, including passkeys, ahead of the planned retirement of SMS as a first-factor sign-in option from February 2027.
The change forms part of Microsoft’s wider effort to strengthen account security and reduce reliance on authentication methods vulnerable to phishing, fraud and account compromise. Administrators have several alternatives available, including passkeys, QR code authentication, FIDO2 security keys and other authentication methods supported by Microsoft Entra ID.
Organisations Advised to Prepare Before February 2027
Administrators are being encouraged to ensure users are migrated to suitable authentication methods before the February 2027 deadline.
Once the changes take effect, organisations will no longer be able to rely on Microsoft’s native SMS and voice authentication capabilities in the same way, making advance preparation important for businesses and other organisations managing large numbers of Entra ID accounts.
“The retirement of SMS sign-in as a first-factor authentication method applies even when you use Choose Your Own Telephony Provider to continue using SMS or voice as multifactor authentication method,” Microsoft said in a Microsoft 365 Message Center update on Friday.
“If your organization currently uses SMS sign-in for first-factor authentication, migrate users to supported alternatives based on their scenarios.”
Microsoft previously retired SMS first-factor sign-in for Microsoft Entra ID Free tenants in August, citing security risks associated with phishing, fraud and account compromise. SMS sign-in is also no longer enabled for newly created tenants.
Change Applies to Entra ID Workforce Tenants
The retirement is specifically aimed at authentication scenarios involving Microsoft Entra ID workforce tenants.
It does not apply to Azure AD B2C or Microsoft Entra External ID customer identity scenarios, meaning organisations should establish which identity services and authentication configurations they currently use before making changes.
Microsoft has also published guidance for organisations preparing to deploy phishing-resistant passwordless authentication across Entra ID environments.
For UK businesses using Microsoft’s cloud identity platform, the transition could require administrators to review existing authentication policies, identify employees still dependent on telephone-based methods and provide alternative authentication options before the deadline.
Passkeys Becoming the Default Entra ID Authentication Experience
The latest reminder follows Microsoft’s announcement in July that passkeys would begin rolling out as the default authentication experience for its Entra ID enterprise identity service from September.
Passkeys are designed to provide passwordless authentication while offering stronger resistance to phishing attacks. Rather than relying on passwords or codes delivered through text messages, passkeys use cryptographic credentials linked to a user’s device or authentication service.
“As the rollout reaches each organization, users enabled for SMS or voice authentication will automatically be enabled for passkeys, and the next time they perform multifactor authentication, they’ll be prompted to register a passkey,” Microsoft said.
“Following this transition, on February 1, 2027, Microsoft will retire Microsoft-provided telecom delivery for SMS and voice authentication and will no longer offer SMS and voice as a native Microsoft Entra capability”
Admins Can Identify Users Still Relying on SMS or Voice
Microsoft is providing tools to help organisations determine which accounts may be affected by the transition.
Administrators assigned Global Reader, Authentication Policy Administrator or Security Reader roles can use Microsoft’s Entra SMS/Voice Policy Scanner PowerShell script to identify users configured for SMS or voice authentication.
This gives IT departments an opportunity to assess their existing authentication estate and plan migrations before the retirement date.
Organisations that still require telephone-based authentication will need to configure third-party telecom providers through the Microsoft Security Store rather than relying on Microsoft’s native SMS and voice delivery.
Microsoft Pushes Towards Phishing-Resistant Authentication
The retirement of SMS first-factor sign-in and the broader move towards passkeys reflect Microsoft’s push to reduce dependence on authentication methods that can be targeted through phishing and other account takeover techniques.
With the February 2027 deadline approaching, organisations using Microsoft Entra ID workforce tenants have several months to identify affected users, update authentication policies and deploy suitable alternatives. Passkeys, FIDO2 security keys and other supported methods will increasingly form the basis of Microsoft’s approach to secure enterprise authentication.
Graham Greene is a contributor to Dealmakerz, covering news, politics, business, technology, sport, entertainment, and lifestyle. He focuses on clear, accurate reporting and useful information that helps readers stay informed about current affairs and developments that matter to them. His work highlights relevant stories, emerging trends, and key issues, presenting them in a balanced, accessible, and reader-friendly way.
More Stories
Polish Developer Builds App That Detects Nearby Meta Smart Glasses
Google Pics Launches with AI Image Creation and Editing Across Docs, Slides and Drive
Closing Android Apps Could Be Slowing Your Phone and Draining Its Battery